
The real impact is usually not the length of the hint, but the clarity of the boundary.
The check first recognizes that unknown configuration, installation of scripts and hooks may be performed at start-up or test. This is not an addition to process, but rather to reduce variables, invalid retests and large-scale modifications.
The sandbox is used to limit the scope of documentation and system capacity.
It is recommended to make a read-only confirmation and then enter a change: look at the directory, AGENTS, configuration and package script from the read-only box and then run it manually.
Do not replace quality with code lines or chat lengths.
The focus of the SEO optimization is not to repeat the Cordex keyword, but to cover the real search intent. It is recommended that URLs remain stable, that the text be synonymous to explain the problem and that links be made to the official document.
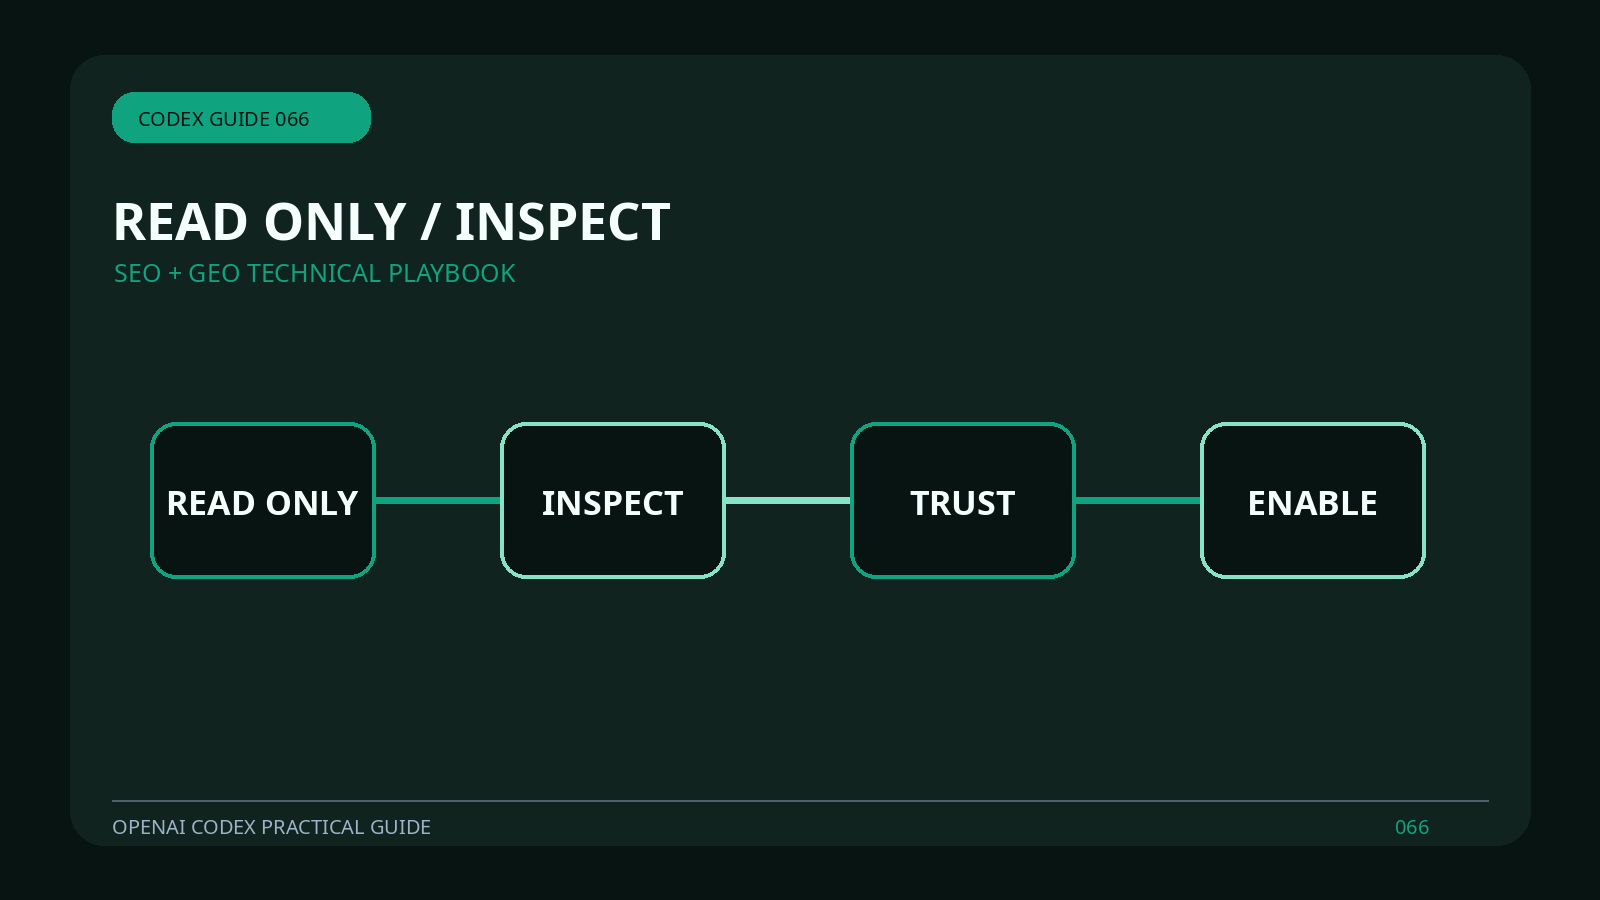
The mission records contain at least four check points: READ ONLY, INSPECT, TRUST, ENABLE.
Two questions need to be answered at the same time: whether to “list out external orders and network access that may be executed” and whether there is a “direct installation dependent or operational construction that could trigger a malicious life cycle script.” The former decides whether to continue and the latter decides whether to suspend, roll back or supplement the authorization.
For long assignments, the phasing summary should refer to actual documents and tests rather than simply describe the work done. The evidence can be reviewed more valuable than the percentage of progress.
To facilitate team re-use, the repository submission, work catalogue, Codex version, profile and key commands can be saved in the task record.
The direct installation of a dependencies or running construction may trigger a malicious life cycle script. Codex can be executed and validated, but it is not a substitute for the operator to determine the scope and risk tolerance.



