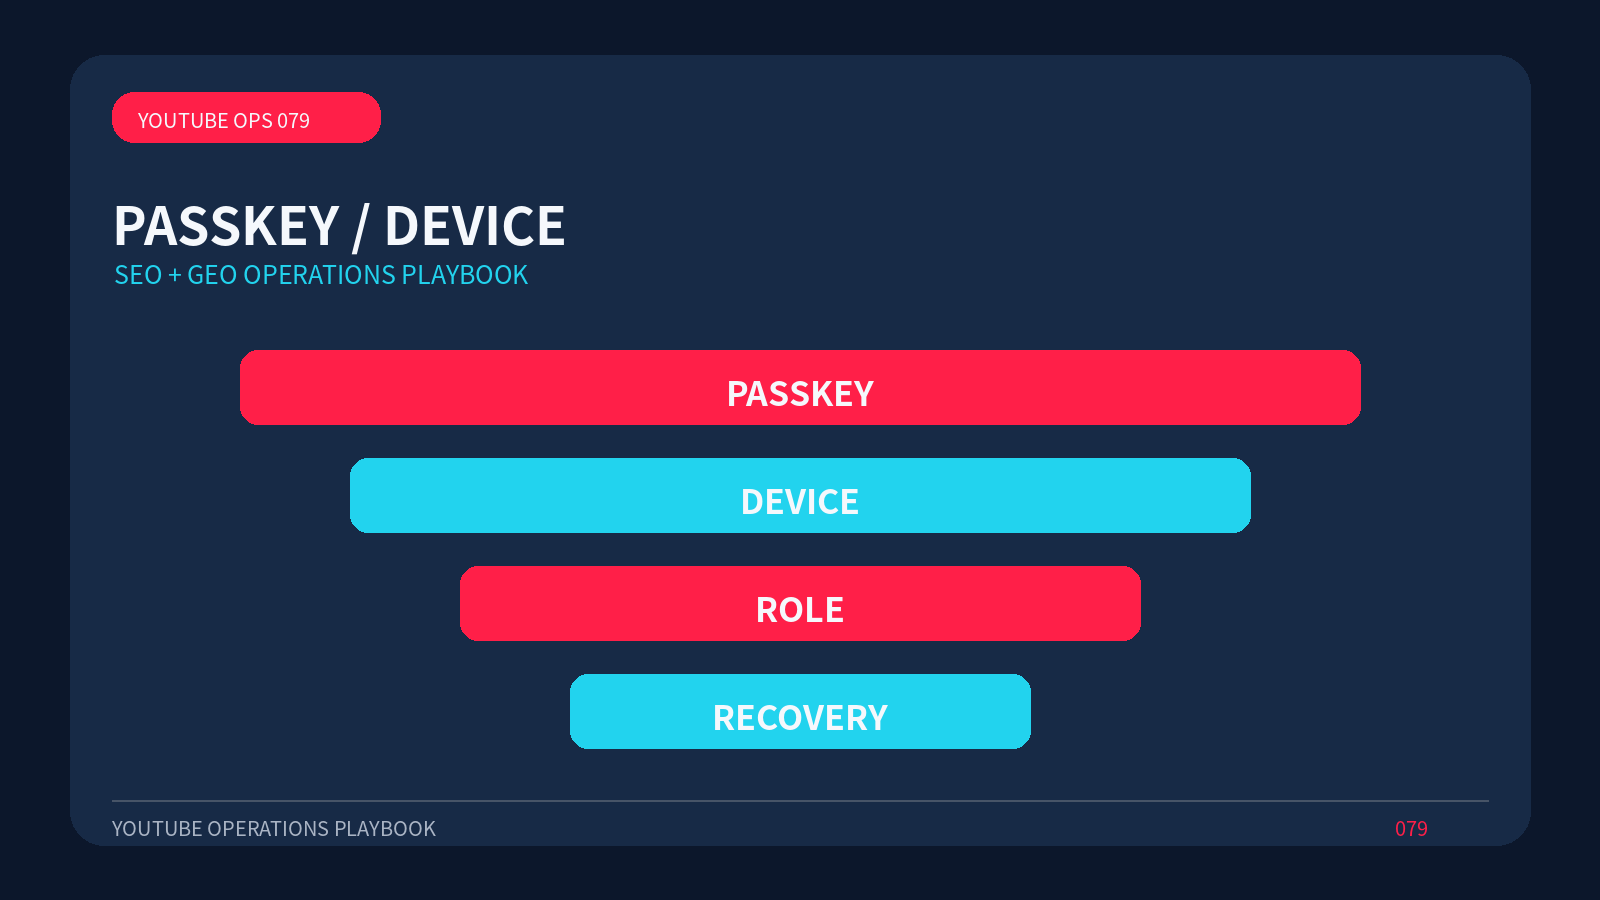
The key to this topic is not to find a fixed value. The real reusable judgement is that security should cover the equipment, authentication, restoration plan and minimum access.
Fishing mail, malicious attachments and password-sharing are common portals to channel hijackings. This suggests that partial optimization cannot be separated from channel audience commitment and asset management.
From the official notes, some common misconceptions can be removed. YouTube’s channel security recommendations include scanning malicious software, using a key or two-step verification, and preparing an account recovery plan.
In order for the YouTube channel to be safe, the project record should include the target market, the material version, the release time and four check points: PASSKEY, DEVICE, ROLE, RECOVERY.
Concrete steps need not be purposive, but focus on using a pass key or two-step validation, scanning malware, limiting the role of a high-authority character and saving the contact to resume. Save previews and version numbers before you go online to facilitate subsequent error correction.
The data level allows for a quarterly review of access, access, restoration of information and exceptional application authorizations.
Videos, subtitles and web pages should have a consistent entity name, but do not need to be copied word for word.
The same taskcard should be used for team work.
Without this information, it is difficult for follow-up staff to judge whether the content is still available.
Pre-production may be preceded by a list of “must” and “not”. The former includes key evidence and limitations, while the latter includes customer privacy, unauthorized assets and unproven commitments.
The scope of application must be made public, since the handing over of the authentication code to a person claiming to be a partner may result in a direct loss of channel control.